AI-Driven Endpoint Detection & Response for Real-Time Threat Containment
If one infected device is found, it can be contained. If they are left to infect other devices for hours they can spread and cause problems across your network. Aavex uses endpoint detection and response to detect compromise on individual endpoints and automatically contain it.
Why the Endpoint Is Where Most Attacks Start
Typically, laptops, workstations, and servers will be the initial targets. This can be done via a malicious attachment, credential theft, or vulnerable applications. Antivirus solutions are typically used but will only detect known threats. New or behaviour-based attacks will not be detected. Often, by the time a member of staff becomes aware there has been a threat present, it has already lateralized.
Aavex provides real-time behavioural detection using continuous monitoring on endpoints and automated containment.
See How Containment Works
Once a threat has been identified, what happens next will determine whether it is a small incident or a full network breach. Our endpoint protection isolates the infected device, stops any malicious activity, and provides you or us with all the information about the incident, so you don’t have to wait for someone to identify the alert.
What This Actually Watches For
- Known and unknown malware — signature-based detection plus behavioral analysis for threats that don’t match a known pattern
- Unauthorized file changes — file integrity monitoring flags tampering with critical system or data files
- Suspicious process behavior — activity that looks like an attack pattern even if the specific threat hasn’t been seen before
- Data exfiltration attempts — controls that flag or block sensitive data leaving a device unexpectedly
Built for Teams Without a Dedicated Endpoint Security Function
Running an EDR platform well takes tuning, monitoring, and someone available when it fires an alert at 2 a.m. Aavex handles all of that, so you get enterprise-grade endpoint protection without staffing for it. This fits particularly well for:
- Businesses with remote or hybrid staff, where devices connect from outside a traditional network perimeter
- Organizations relying on basic antivirus that hasn’t kept pace with modern attack techniques
- Teams that need device-level compliance controls (file integrity monitoring, data control) without building that capability in-house
- Growing businesses adding devices and locations faster than their IT team can manually secure each one
How Protection Runs, Step by Step
| Step | What Happens |
|---|---|
| Data collection | Telemetry is gathered continuously from endpoints, servers, cloud workloads, and IoT/OT devices |
| Enrichment | Collected data is enriched with identity, threat intelligence, and vulnerability context |
| Detection | AI and machine learning analyze enriched data for compromise indicators and behavioral anomalies |
| Alerting | Detailed incident insights are generated automatically when a threat is identified |
| Containment | Automated response isolates and halts threats in real time, minimizing damage and downtime |
| Ongoing monitoring | Continuous visibility keeps watch across the environment, even as devices and users change |
Technology Behind This Service
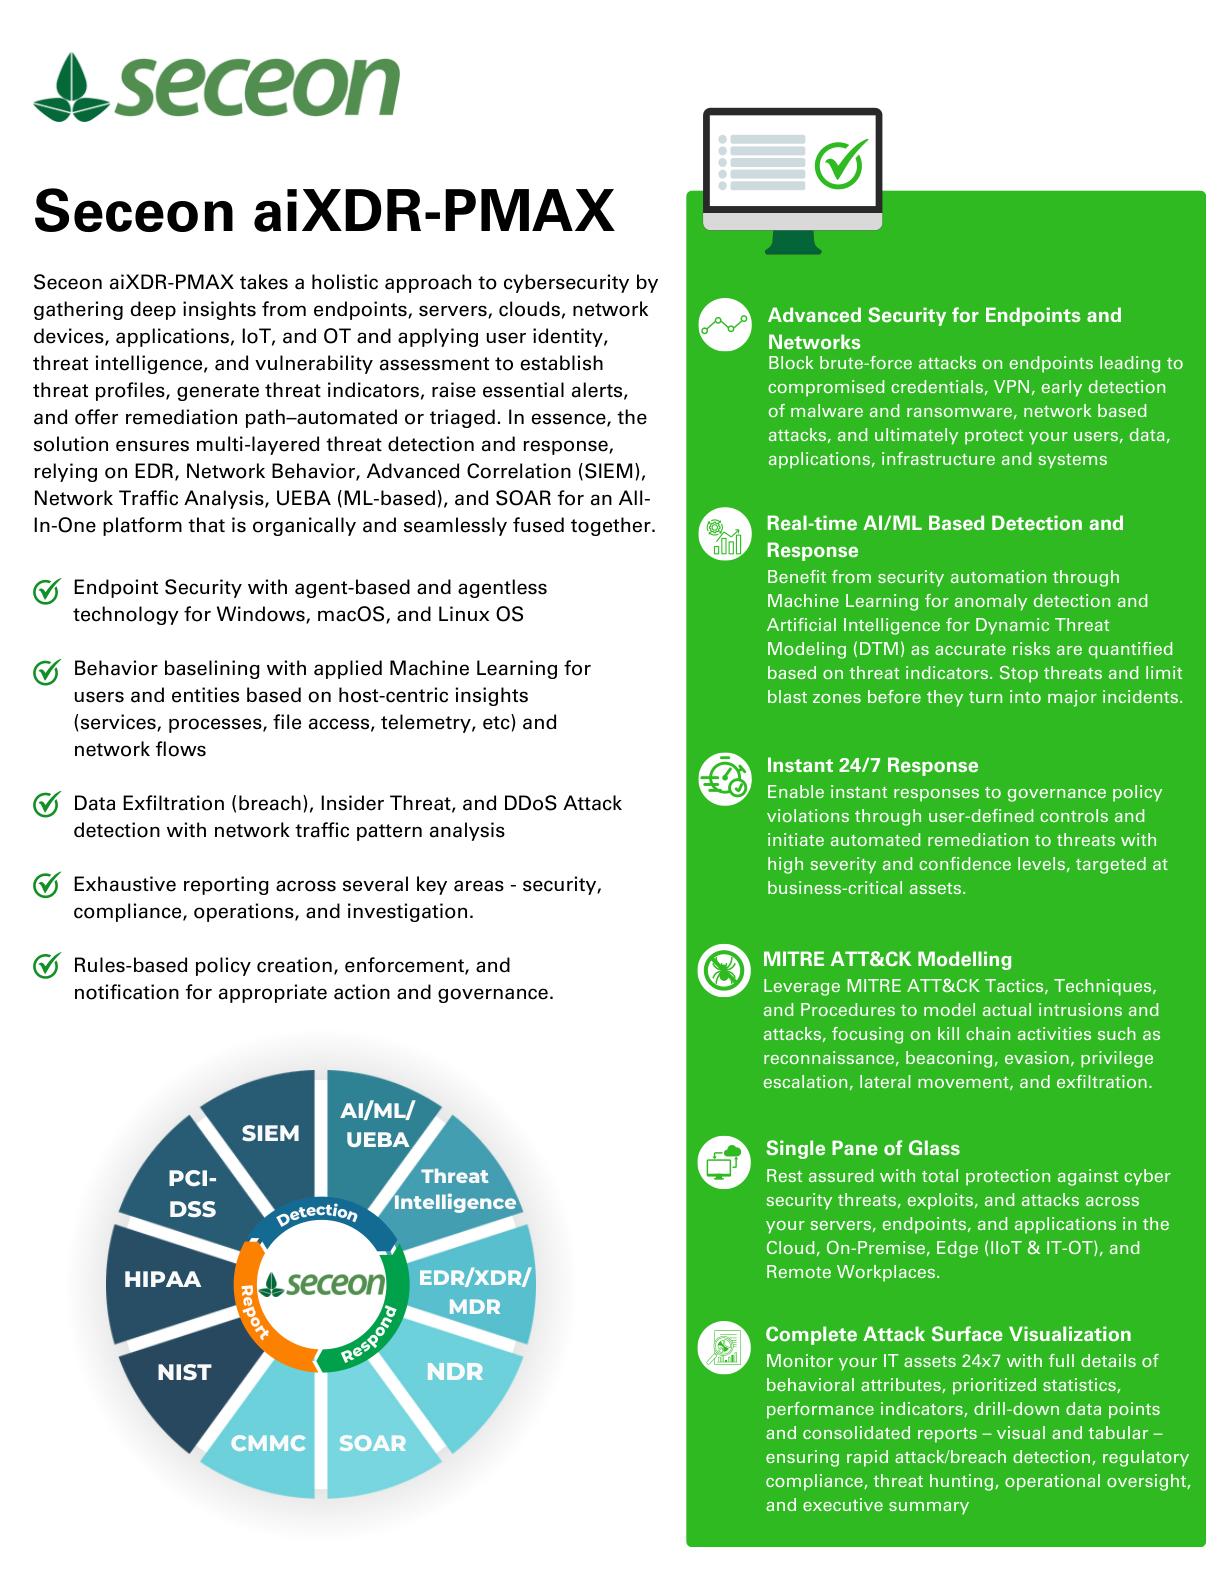
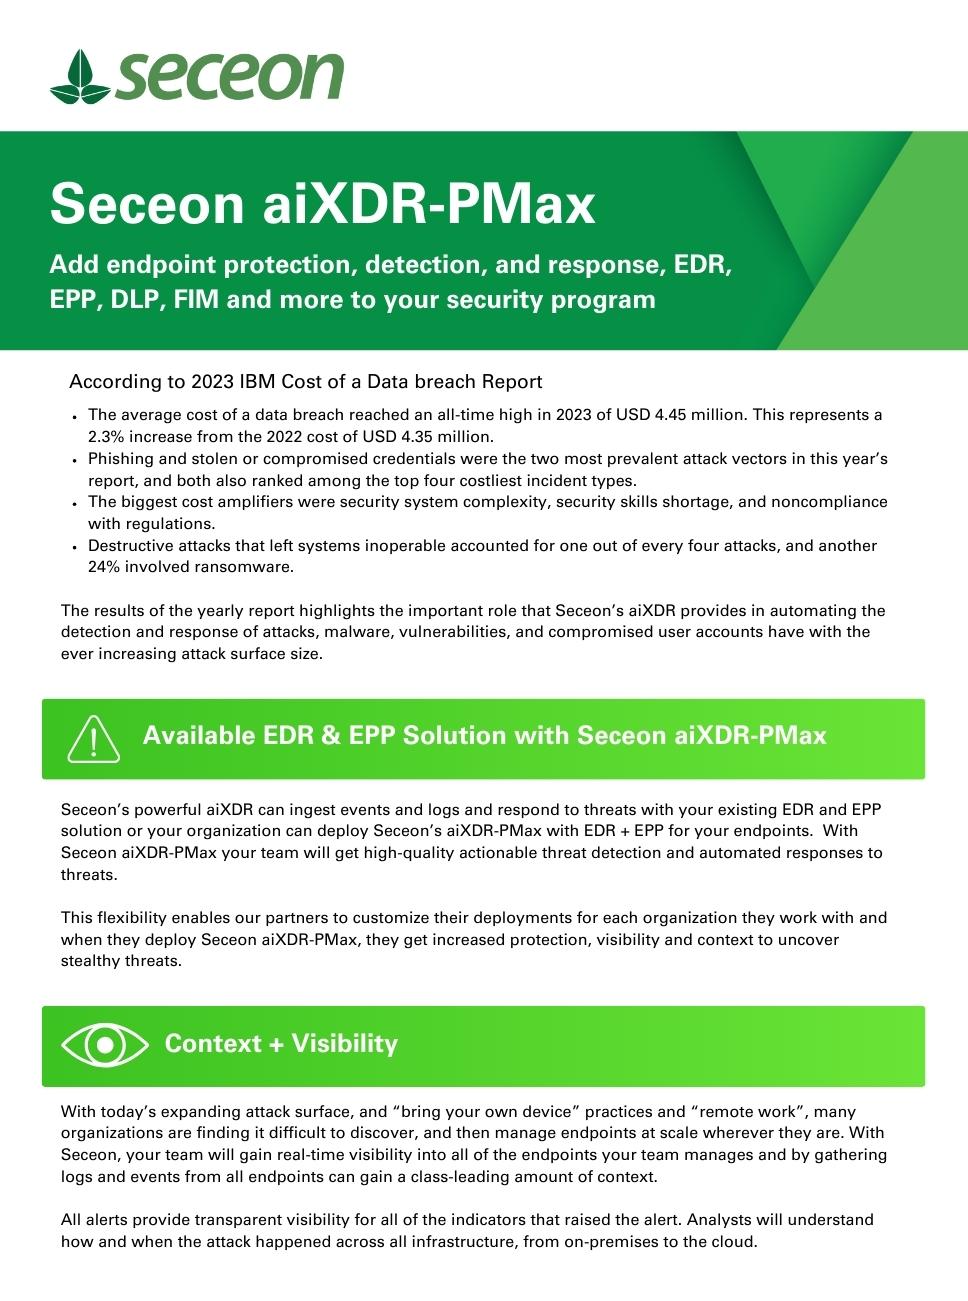
Built on the Seceon aiXDR-PMax solution, our service combines endpoint threat detection, XDR and automated containment. We configure, tune and monitor the technology to provide detection and response capabilities without the need to manage the underlying tooling.
Discover More with Our Datasheet
Read the datasheet to see the full picture of how this endpoint protection works — real-time detection, automatic containment, and the AI-driven analysis behind both.
Download it below, or request a walkthrough if you’d rather see how it applies to your own environment.
What Clients Say
OFFICE LINE
EMAIL US